
Zero-Knowledge Architecture
Your keys and your private data live on your device. Flowsta physically cannot access them - and neither can anyone in between.
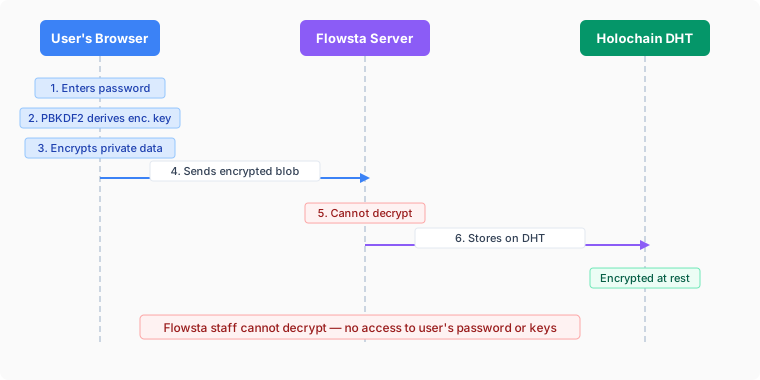
No password exists on any server. The only password is the one that unlocks your Vault, and it never leaves your device. Your identity is a set of cryptographic keys derived from your 24-word recovery phrase, held on your device in Flowsta Vault. Flowsta's server never sees the phrase, never sees the keys, and stores nothing it could decrypt.
What Only You Hold
Everything sensitive stays on your device:
| Data | Where it lives |
|---|---|
| 24-word recovery phrase | With you - written down, never transmitted |
| Ed25519 device keys | Derived on-device from the phrase via HMAC-SHA256 |
| Private records | Sealed (encrypted) on your device in Flowsta Vault |
| App data backups | Stored locally by the Vault |
Sealed private records do not gossip to Flowsta or to anyone else. They never leave your device unless you export them yourself.
What Flowsta Can See
Flowsta's server stores only what it needs to route sign-ins:
| Data | Purpose |
|---|---|
| Email hash | Look up your identity at sign-in - a one-way SHA-256 hash, not your address |
| Lookup metadata | Recovery lookup hash, agent public key, DID |
| Display name, username & profile picture | Your public profile, served by Flowsta's API and cached for flowsta.com and app sign-ins (you chose to make these public) |
| OAuth consent records | Audit trail of which apps you authorized |
| Usage counters | Active-connection and signing-quota counts, keyed by an opaque pseudonym - see What the Vault Sends Home |
What Flowsta does not hold for a Vault identity: no password hash, no keys, no recovery phrase, no private records. There is nothing on Flowsta's servers that could decrypt your data - not for staff, not for attackers, not for anyone.
Public, Verifiable Data
Two kinds of data are public by design, on Flowsta's tamper-proof network, built on Holochain:
Identity DNA (Public)
Your public identity record - and nothing that identifies you as a person:
- Your DID (
did:flowsta:<agent key>) and agent public key - Created and updated timestamps
- Site memberships and agent links (identity attestations)
Display name, username and profile picture are not on the network. They are held by Flowsta's server as your public profile (see above) and served to flowsta.com and to apps you authorize. Your DID never changes for the life of your identity.
Signing DNA (Public)
Signatures created by Sign It:
- Ed25519 signatures over SHA-256 file hashes
- Signing intent (
Authorship,Approval,Witness,Receipt,Agreement) - Content rights manifests (license, AI training policy)
- Perceptual hash bands (for fuzzy matching of modified files)
- Revocation entries (signed by the original signer)
Signatures are public and permanent by design - that's how verification works. The DNA holds no name, no email and no file - only hashes, signatures, and whatever public note or thumbnail the signer chose to attach. See Sign It for details.
How Sign-In Works Without a Password
Signing in is a cryptographic proof, not a shared secret:
- Your device requests a one-time challenge:
POST /auth/vault/challenge - Flowsta Vault signs the challenge with your identity key - derived from your recovery phrase, which never leaves your devices - and, from 1.6.0, with this device's own key beside it
- Your device submits the signature:
POST /auth/vault/token - The server verifies the signature against your public key and issues a JWT plus the
flowsta_sessionSSO cookie
The server learns that you control your key. It learns nothing else. There is no credential to phish, reuse, or leak from a database breach.
Key Derivation
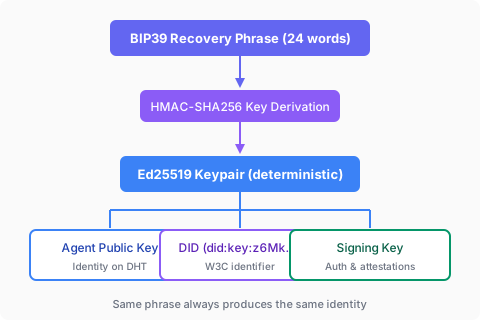
Your 24-word BIP39 recovery phrase deterministically generates your keypair via HMAC-SHA256. That means:
- Your recovery phrase restores your identity on any device - install Flowsta Vault, enter the phrase, and your keys and DID come back exactly as they were
- No key escrow or key recovery service is needed (or possible)
- Flowsta never sees the phrase - derivation happens entirely on your device
Why This Matters
Most identity providers sit between you and everything you do: they hold your password hash, your session keys, and often your data. A breach of the provider is a breach of you.
Flowsta is built so there is no one in between - not even Flowsta. The server can't be compelled, hacked, or tempted to reveal what it never had. Your keys prove who you are; your device holds what's yours; the public network verifies what you choose to publish.
Implications for Developers
When you receive user data through OAuth:
- Public data (display name, username, DID, agent public key) is readable by Flowsta
- Email is shared only if the user explicitly grants the
emailscope - No data mining - Flowsta cannot analyze user private data for any purpose, because it never has it
Next Steps
- Data Portability - How users export and restore their data
- Sessions - Token management and lifetimes
- OAuth Security - Security best practices for developers